Thrilling! Thank you OPM!

OPMI kept hearing about the data breach at the OPM. I thought to myself, “no big deal,” because I’ve never been a government employee. But then one of the articles I read spoke about a particular form. The form number seemed familiar.

Out of curiosity I checked my encrypted drive.

AHHHH SHIT!!!!

Yep, that’s a form I filled out while I was working for a government contractor.

DAMN! Checking some of the other forms and sure enough! There’s a TON of information that I provided to my employer. I’m sure that that information got sent at some point to the OPM, and is now in the hands of the Chinese.

I’m sitting here looking at my encrypted volume that contains this information thinking a couple of things.
CybersecurityFirst, I’m wondering why I take the security of this information so seriously? Why is it that I’ve spent the money to secure my data and theirs (some of the information contained in the forms I filled out for them also contains information that relates directly to THEIR projects) and am mindful of what data I have “live” on my system and what data I keep in cold storage? Cold storage in my life is something (like a drive) that is archival, MUST be turned on or attached directly to my computer and is encrypted.

Second, If I can secure my data with COTS (Commercial Off The Shelf) software why can’t our government?

Third, Why is the United States Government data vulnerable in the first place? We KNOW the safest computers are computers which are not connected to a network. Granted, that’s impractical because the government must share data.
Hearings

BUT  it is possible to isolate critical subsystems. One way to do that, don’t allow employees to transport any data offsite. No USB memory sticks or other media, and laptops are available only to those employees who absolutely need mobility. Employees using those laptops have VPN access to the corporate systems and for the most part those laptops when connected to the corporate VPN are Terminals in the old school meaning of terminals. ie dumb as a rock.

The point I’m making here is that the need for computer & network security isn’t new.  So why the hell hasn’t our government kept up with the needs for security?

Having seen the way government contracts work, I have a guess.

redtape

Imagine a situation where a bunch of cooks get in the soup and specify all manner of equipment down to the smallest detail. Once finished,  the specification goes from committee to committee and after a year or two the spec is approved, money is appropriated and the funds become available.

Our happy IT guys call a government approved vendor of equipment, and are told that equipment isn’t available anymore. Or worse yet, the equipment or software can be purchased but now it’s a custom build and will be 50% more expensive than the original product and by the way have significantly fewer capabilities than current off the shelf products costing significantly less than the originally specified equipment or software originally sold for.

Old terminal

So in the one case the specification process starts over again. In the other case the “approved equipment” is less capable,  yet more expensive, than the machine a hacker in China purchased on the internet yesterday.

Rather than the committees addressing the fundamental problem in terms of appropriations and approvals they’re content to keep failing. Meanwhile the security of government systems continues to fall further and further behind.
This isn’t a partisan issue. Regardless of what the administration might say. This is an epic systemic failure on the part of an entity that has access to all of our private data. A.K.A The United States Government.
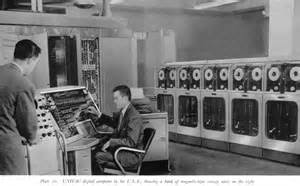
UNIVAC

How do you solve this problem?

The simplest way is to allow the IT people, The REAL IT people, not the morons that built the healthcare.gov site, say “we need a router and after figuring out which is the best unit for the money… They BUY IT!

That should go for a single router or a RACK of routers.

Does Dianne Freakin Feinstein have a clue about the difference between a CISCO and a Barracuda? NO!

So why are people like Feinstein reviewing and voting on these appropriations bills or worse yet wasting time and money having hearings about shit they’ll never understand, when they should be letting the professionals do the job? You can tell pretty darn fast if an IT dept. is pissing money away and a quarterly budget review (again by IT pros who know what’s needed and what it costs) would keep the expenditures in check and at the same time maintain security.

I’ve got another dose of BAD news for you dear reader…
JihadiHacker

The longer our leaders put off fixing the government IT infrastructure, the more expensive it’s going to be.

Think about putting off having your brakes fixed on your car.

Brake pads cost $45 a wheel, Brake ROTORS cost $1000 a wheel. Most of us average folks learn the hard lesson, it’s always better to spend the $180 rather than spending the $1180. We all learn it once!

We never make that mistake again unless we’re wealthy, elitist,  over-educated, dumbasses.

Unfortunately, most of our politicians are the latter kind of people not the former.


Update 2015 06 19

As more comes out about this breach, I think it’s clear that the government IT people are not up to the challenge.

Here is a line to an ars Technica article titled Encryption “would not have helped at OPM says DHS official”

Below is the article minus the video.


Encryption “would not have helped” at OPM, says DHS official
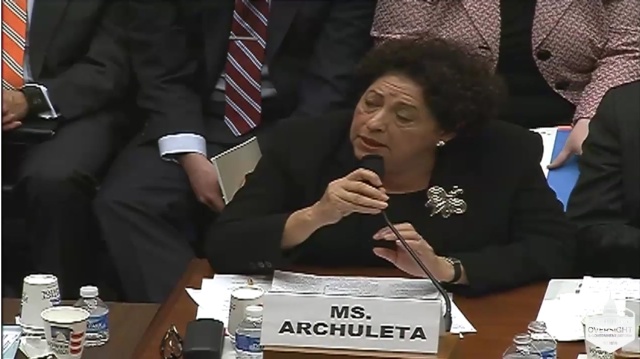
archuleta-opm-640x359

Office of Personnel Management Director Katherine Archuleta would be happy to discuss the particulars of the OPM brief with Congress—in a classified briefing.

CSPAN

During testimony today in a grueling two-hour hearing before the House Oversight and Government Reform Committee, Office of Personnel Management (OPM) Director Katherine Archuleta claimed that she had recognized huge problems with the agency’s computer security when she assumed her post 18 months ago. But when pressed on why systems had not been protected with encryption prior to the recent discovery of an intrusion that gave attackers access to sensitive data on millions of government employees and government contractors, she said, “It is not feasible to implement on networks that are too old.” She added that the agency is now working to encrypt data within its networks.

But even if the systems had been encrypted, it likely wouldn’t have mattered. Department of Homeland Security Assistant Secretary for Cybersecurity Dr. Andy Ozment testified that encryption would “not have helped in this case” because the attackers had gained valid user credentials to the systems that they attacked—likely through social engineering. And because of the lack of multifactor authentication on these systems, the attackers would have been able to use those credentials at will to access systems from within and potentially even from outside the network.

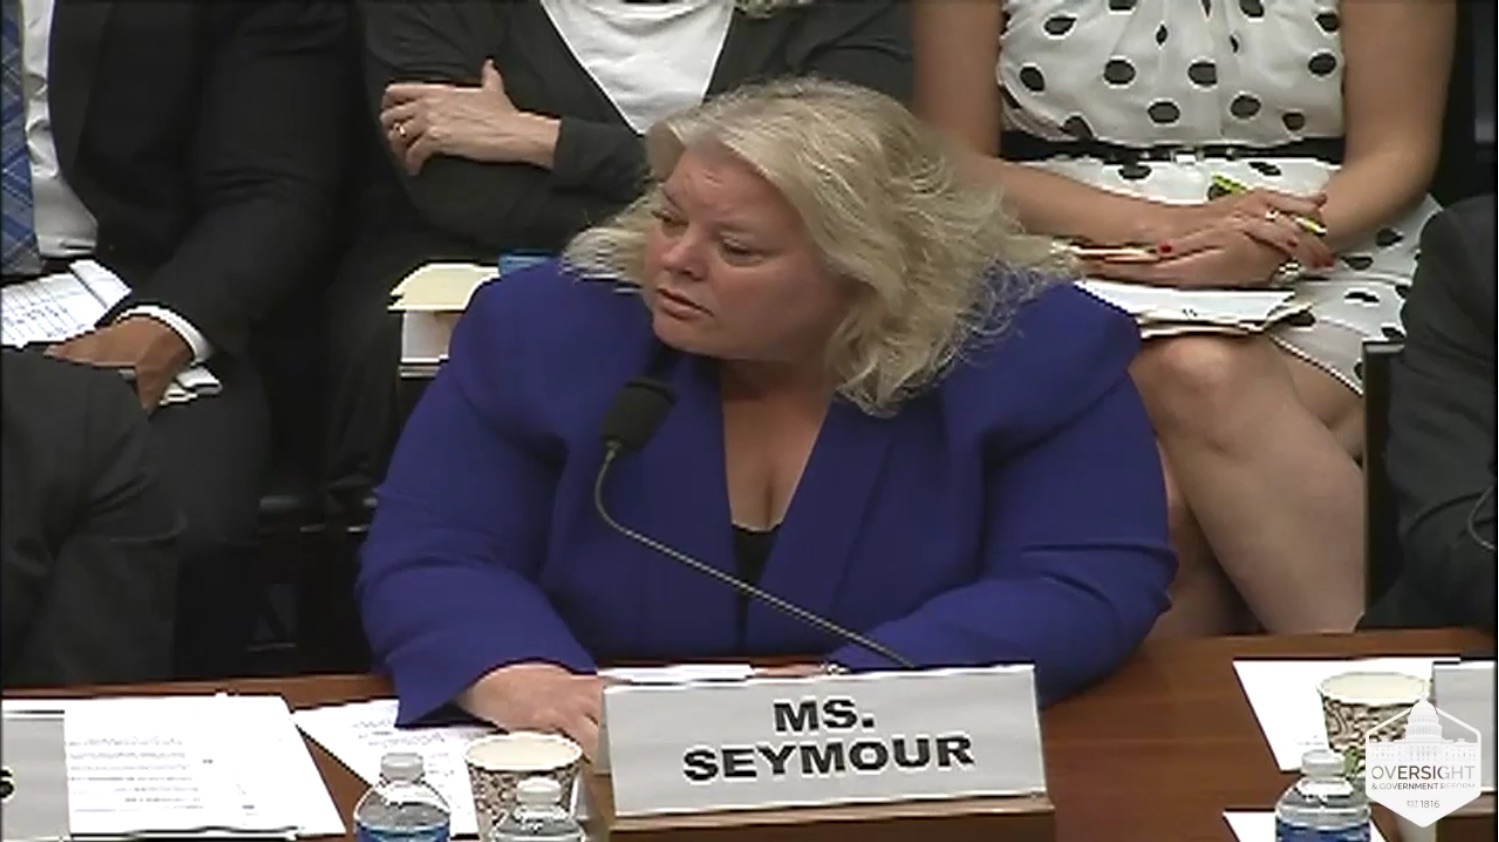
House Oversight Chairman Jason Chaffetz (R-Utah) told Archuleta and OPM Chief Information Officer Donna Seymour, “You failed utterly and totally.” He referred to OPM’s own inspector general reports and hammered Seymour in particular for the 11 major systems out of 47 that had not been properly certified as secure—which were not contractor systems but systems operated by OPM’s own IT department. “They were in your office, which is a horrible example to be setting,” Chaffetz told Seymour. In total, 65 percent of OPM’s data was stored on those uncertified systems.

Chaffetz pointed out in his opening statement that for the past eight years, according to OPM’s own Inspector General reports, “OPM’s data security posture was akin to leaving all your doors and windows unlocked and hoping nobody would walk in and take the information.”

When Chaffetz asked Archuleta directly about the number of people who had been affected by the breach of OPM’s systems and whether it included contractor information as well as that of federal employees, Archuleta replied repeatedly, “I would be glad to discuss that in a classified setting.” That was Archuleta’s response to nearly all of the committee members’ questions over the course of the hearing this morning.

At least we found it

Archuleta told the committee that the breach was found only because she had been pushing forward with an aggressive plan to update OPM’s security, centralizing the oversight of IT security under the chief information officer and implementing “numerous tools and capabilities.” She claimed that it was during the process of updating tools that the breach was discovered. “But for the fact that OPM implemented new, more stringent security tools in its environment, we would have never known that malicious activity had previously existed on the network and would not have been able to share that information for the protection of the rest of the federal government,” she read from her prepared statement.

Dr. Ozment reiterated that when the malware activity behind the breach was discovered, “we loaded that information into Einstein (DHS’ government-wide intrusion detection system) immediately. We also put it into Einstein 3 (the intrusion prevention system currently being rolled out) so that agencies protected by it would be protected from it going forward.”

But nearly every question of substance about the breach—which systems were affected, how many individuals’ data was exposed, what type of data was accessed, and the potential security implications of that data—was deferred by Archuleta on the grounds that the information was classified. What wasn’t classified was OPM’s horrible track record on security, which dates back at least to the George W. Bush administration—if not further.

A history of neglect

During his opening statement, Chaffetz read verbatim from a 2009 OPM inspector general report that noted, “The continuing weakness in OPM information security program results directly from inadequate governance. Most if not all of the [information security] exceptions we noted this year result from a lack of leadership, policy, and guidance.” Similar statements were read from 2010 and 2012 reports, each more dire than the last. The OPM Office of the Inspector General only began upgrading its assessment of the agency’s security posture in its fiscal year 2014 report—filed just before news of a breach at a second OPM background investigation contractor surfaced.

Rep. Will Hurd (R-Texas), a freshman member of Congress, told the OPM executives and the other witnesses—DHS’ Ozment, Interior Department CIO Sylvia Burns, the new US CIO Tony Scott, and OPM Assistant Inspector General Michael Esser— that “the execution on security has been horrific. Good intentions are not good enough.” He asked Seymour pointedly about the legacy systems that had not been adequately protected or upgraded. Seymour replied that some of them were over 20 years old and written in COBOL, and they could not easily be upgraded or replaced. These systems would be difficult to update to include encryption or multi-factor authentication because of their aging code base, and they would require a full rewrite.
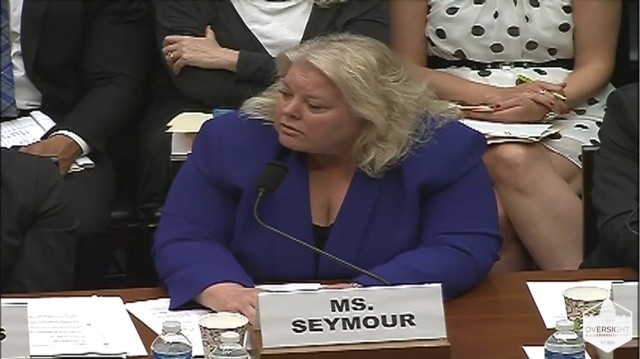
seymour-opm-640x359

Enlarge / OPM CIO Donna Seymour said that systems couldn’t simply have encryption added because some of them were over 20 years old and written in COBOL.

Personnel systems have often been treated with less sensitivity about security by government agencies. Even health systems have had issues, such as the Department of Veterans’ Affairs national telehealth program, which was breached in December of 2014. And there have been two previous breaches of OPM background investigation data through contractors—first the now-defunct USIS in August of last year, and then KeyPoint Government Solutions less than four months later. Those breaches included data about both government employees and contractors working for the government.

But some of the security issues at OPM fall on Congress’ shoulders—the breaches of contractors in particular. Until recently, federal agents carried out background investigations for OPM. Then Congress cut the budget for investigations, and they were outsourced to USIS, which, as one person familiar with OPM’s investigation process told Ars, was essentially a company made up of “some OPM people who quit the agency and started up USIS on a shoestring.” When USIS was breached and most of its data (if not all of it) was stolen, the company lost its government contracts and was replaced by KeyPoint—”a bunch of people on an even thinner shoestring. Now if you get investigated, it’s by a person with a personal Gmail account because the company that does the investigation literally has no IT infrastructure. And this Gmail account is not one of those where a company contracts with Google for business services. It is a personal Gmail account.”

Some of the contractors that have helped OPM with managing internal data have had security issues of their own—including potentially giving foreign governments direct access to data long before the recent reported breaches. A consultant who did some work with a company contracted by OPM to manage personnel records for a number of agencies told Ars that he found the Unix systems administrator for the project “was in Argentina and his co-worker was physically located in the [People’s Republic of China]. Both had direct access to every row of data in every database: they were root. Another team that worked with these databases had at its head two team members with PRC passports. I know that because I challenged them personally and revoked their privileges. From my perspective, OPM compromised this information more than three years ago and my take on the current breach is ‘so what’s new?'”

Given the scope and duration of the data breaches, it may be impossible for the US government to get a handle on the exact extent of the damage done just by the latest attack on OPM’s systems. If anything is clear, it is that the aging infrastructure of many civilian agencies in Washington magnify the problems the government faces in securing its networks, and OPM’s data breach may just be the biggest one that the government knows about to date.


<END>

I’ve been feeling Compressed

PADI 2014 Oct 12

No, not as in diving compressed, (although I could use some underwater time). Any Divers out there wanna get wet? [Thanks to PADI for the nifty photo]

My compression stems from issues in my life.

As I’ve mentioned before, I share internet with the next door neighbor. Generally this isn’t a problem,  they’re using an old Windows based machine that I suspect is rife with malware. This doesn’t really affect me, except that when that machine logs onto the network it sucks up pretty much all the available DSL bandwidth.

For the non techies… The internet gets really slow.

Most of the time, even that doesn’t bother me unless I’m streaming a movie or something. But it reminds me that I’m not alone, and someone else has the ability to affect my life through my own niceness.

Then there’s the ugly assed fence which focuses my vision on their back yard, making me to be completely unable to ignore all the kids stuff, trampoline, monkey bars, various toys scattered about, and the pile ‘o junk stuffed in the corner.

IMG 0309

This fence also makes me feel that I have no privacy because it’s a constant reminder that there are kids there, even when they’re not out screaming, squabbling, or using the trampoline to jump up above the fence to ask me what I’m doing out on my deck. I can’t look past it, god knows I’ve tried. The 7ft tall monstrosity is THERE  protecting the children from… what? The occasional wayward hiker?

Then there’s the ceiling fan in my office. You see, the neighbors apparently put up a new ceiling fan in their house, and they left the unit’s code set to default. (Lots of new ceiling fans have these nifty remotes that allow you to change the speed of the fan and / or control the light in the fan.)

The problem is that when you put one of these fans in, you really should choose a new code other than the default one. Guess how I found out the electrician that built this house hadn’t bothered to change the code?

You guessed it. The great fan war started this summer. There are three neighbors that could possibly be close enough to control my office ceiling fan. One house is under going major remodeling. Since that place is gutted, I scratched them off the list. The other neighbor isn’t likely to have made any real changes, since she’s cold all the time. Which leaves the next door neighbors!

IMG 0362

Dammit! They’re jacking my internet up, have destroyed the view, have left me feeling like I’m having to accommodate their kids, “Asked” that we hose down our back yard every day during a drought while letting our plants die because she was pregnant and her nose was too sensitive, and finally…

Because they don’t want to figure out why their new fan isn’t working quite right, I’m the one that has to get up on a ladder with a screwdriver and a spring hook, (a spring hook looks a lot like a dental tool its sharp and pointy with a slight hook at one end. Great for flipping tiny little switches.) to manhandle 70lbs of ceiling fan to change the code to something they’re not using. 

But then it continues…

Once I’ve got the fan issue fixed, I think, “hey its time for me to rearrange the office” and so I begin that process only to find that my other half has systematically occupied every single open space in both closets, the filing cabinet, and a substantial portion of the basement with… for want of a better term CRAP! 

There’s no way for me to put my stuff out of the way or reorganize my stuff because his stuff is literally everywhere.

SO after grumbling about living with the equivalent of a 13 year old packrat, LOUDLY.  I start whipping through my shit and tossing anything that isn’t nailed down and functional. 

But the whole time I’m thinking, why am I the one that’s adapting to the situation AGAIN. 

I find myself thinking, “Maybe I should just pack whatever shit from this house that I want, and that will fit in my damn car and that will be MY space. Perhaps my life will be easier if I just allow the forces in my life that are conspiring to compress me into a tight little space, win. Then everyone will be happier and I’ll finally have some peace. Maybe I should sell every vehicle I own, buy a pickup truck with a tonneau cover (I don’t like camper shells) and be a true nomad, wandering towns and highways randomly. I’ll stop in interesting places do piece work for cash then move on. Maybe I should become ’That Guy’, the stranger, the scary dude in the corner of your local bar. ”

Then again maybe all this is just another way for the universe to tell me “Its time to move on.”

This one I couldn’t let pass, it really pisses me off. NSFW


5 year old rape victim dies in Herat

NewImage

I originally saw this on Breitbart but followed it back to the Afghanistan Times (the link above).

Frankly, my brain rebooted.

There are so many things going through my head I’m not sure I can cogently prioritize them all.

The doctors at the hospital covered the cause of death, describing it as choking, instead of butfucking a 5 year old child to death. The boys, (I sincerely question what is meant by “boys” in this context) have been arrested but will probably be found innocent of the rape charges.

It’s the other details that make me positive we should have nuked the entire area, carpet bomb style. Sterilize the whole country, make it visible from space as a glowing wasteland, but I get ahead of myself.

NewImage

The hypocrisy of these people is overwhelming. At the same time a 15 year old girl can be beaten and tortured by her in-laws for refusing to become a prostitute, apparently the victims of rape are often considered criminals and immoral because they were forced to have sex prior to wedlock.

THE VICTIMS??? What about the owners of the DICKS that violated children?

While I was trying to find the article about this boy on the Afghanistan Times site, I found another article about a three year old girl being raped by an adult man. Again, it looked like he might be held responsible for murder.

Then I read in the Breitbart article that older men sometimes  take on pre-pubescent MALE lovers in some bullshit cultural thing called “bacha baazi.”

WHAT?!?!? I thought it was customary for islamic “high morality” cultures to mutilate and then kill any homosexual. In this way they prevent the sullying of their “Religion of Peace” and preserving the high moral standards we’ve all come to know and “appreciate” from the followers of Islam.  Yet, here we have a cultural institution wherein homosexual behavior is apparently acceptable as long as it’s an older man with a boy whose balls haven’t dropped.

SORRY… Putting your dick in a boy, is homosexual behavior regardless of the age of the boy or how many wives you have.

Singularitysphere1

What are we supposed to believe here, that the man didn’t realize he was fucking a boy… IN THE ASS?

What happens if the boy happens to develop a preference for male sex when he becomes an adult?

Well, we know that answer.  Presumably after enduring years of shame and humiliation, he gets caught with another man and then endures being imprisoned, mutilated, then fucked by the prison guards before he’s taken out and beheaded, stoned, or hung. 

Singularitysphere2

Were I twenty years younger I’d sign up for college, then become a physicist with but one goal in mind.

I’d find a way to create a singularity sphere like the ones in The Arrival.  Then I’d happily drop a dozen or so of those puppies all over Afghanistan.

If you don’t remember, these things were flat cool. They lift off, scan the area, then suck everything into a singularity. 

No fuss, no muss, probably nothing more than just a brief wink of X-ray radiation as the surrounding matter disappears into the singularity’s event horizon. 

Totally excellent devices for urban renewal or to dispose of a vermin problem.

Make no mistake, Religion/culture of peace and morality, MY ASS!

No more funding for these animals, Let them all wither and die in a shithole of their own making. These people seem to know nothing but curelty, hatred and violence.  Perhaps, since we have no singularities handy, could we at least drop a few big assed rocks on ‘em from orbit?

I used to apply the lesson learned when God destroyed Sodom and Gomorrah, Spare the innocent…

Now I’ve come to think that euthanasia in these shitholes might be a more merciful option. 


And to lighten things up. Here’s Andrew Klavan on political correctness.

Been out of it for a couple of days… All I can say is DAMN!

NewImage

My ISP was having some difficulties with packet loss and their problems were affecting my ability to get email and upload to the blog.

Paraphrasing Poltergeist 

“I’mmmm BAAACCK!”

The question is what do I talk about first?

NewImage

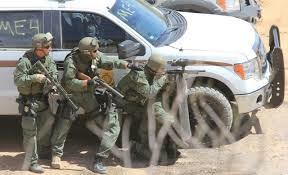
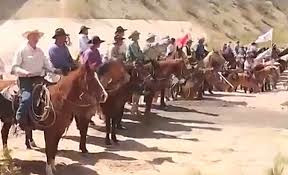
The Bundy Ranch v the BLM?

I hate to even think about what could have happened if someone had squeezed off a shot during that standoff. That’s how really bad things happen really damn fast. I personally don’t think Mr Bundy has a leg to stand on legally. OF more concern to me is that we had an armed standoff at all. 

NewImage

When you start looking at issues surrounding the Bundy standoff. You can’t help but stumble over reports of other events where one could say that the US Government is overstepping its authority and behaving very much like a totalitarian entity.

There are currently issues over land between Texas & Missouri due to the ever changing nature of a river that had traditionally marked the boundary line between the states and ranchers in the area. The BLM is taking an interest and stands to usurp something like 90,000 acres without compensating either the states or the landholders.

NewImage

The EPA is attempting to assert control over many bodies of water, including watering ponds on farms and ranches. They are also making noises about assuming control of dry or seasonal creek and river beds.

Meanwhile The Border patrol has become a nuisance to Arizona ranchers whose property abuts the buffer zone between the US / Mexico boarder They’re doing things like cutting fences or leaving gates open without so much as a “by your leave.” 

NewImage

These supposed events are concerning because they’re in general, never picked up by the main stream media but are reported in local area papers. On an individual basis these seem like minor local issues but when you view them from the “orbit” of the internet it does start to look like a quiet conquest.

With government oversight, come government control. With government control, come fees, fines, and increased taxation (whether it’s called a tax or not.) This seems to be the source of the underlying embers that almost burst into flames at the Bundy ranch.

NewImage

The FDA is being reported as sticking their noses into a long standing arrangement (100+ years) between Beer Brewers and farmers regarding grain. The Beer uses the grain to make beer, then the waste material is usually given to farmers / ranchers to mix with feed stock. This arrangement takes care of the waste without requiring anything other than a farmer / ranchers willingness to haul the used grain away.

Now, the FDA is wanting to regulate this equitable arrangement in the name of public health even though there has never been an instance where the public or the animals have been harmed. Some old traditions bacme old traditions due to the test of TIME. It’s not in the best interests of Farmers or Ranchers to engage in an activity that is detrimental to their livelyhoods. So does the FDA really need to be involved? Probably not, but you can expect for their fees and inspections and whatever the hell else they’ll do to drive up the cost of a beer, and possible the cost of food too.

NewImage

The newest revelations about the IRS internal memos?

Just WHO is Lois Learner afraid of? She claims she’s in fear for her life and that’s why she doesn’t want to testify. REALLY? Can’t her employer The United States Government protect her & her family? Or is it the US Government that she’s afraid of?

The Ukraine?

Images

Does anyone really believe that Vladimir Putin is concerned in the least about what President Stompy Foot thinks? Don’t get me wrong Putin is not a nice guy but he’s doing what he things is best for his country ( Or Himself) and he’s not in the habit of asking permission. 

Potential for World War III?

There have been some writers comparing the flashpoint issues for WWI and WWII to what’s happening in the Ukraine.

I’m not sure that I completely agree with their assesment that WWIII could be in the offing but the correlations are interesting to read. I doubt Putin would move it to an all out war against NATO but hey no-one thought a strange little houspainter would end up Chancellor of Germany either.

President Obama’s trustworthy polls?

This one cracked me up. Approximately 60% of Americans believe that Obama is actively lying to them one way or another. Now that’s really gotta piss President Finger waver off.

NewImage

The President was on TV again today defending Obamacare and as usual took the opportunity to reiterate that Republicans are BAD and that their continued desire to revisit Obamacare isn’t in the public interest. Whoo Hoo 8 million people signed up. Lets see, there are approximately 313.9 Million people in the US. Does that mean a whopping 3% of the population signed up. Whoooo impressive!

I’d have been more impressed if this 8 million had ALL been previously uninsured people instead of poor schmucks that lost their insurance and had to find something on the exchanges.

I’d have been more impressed if there wasn’t a recent editorial by a lady that had called something like 92 doctors in New Jersey only to find out that her shiny new obamacare card wasn’t being accepted because the doctors didn’t want to deal with the smaller payments obamacare would provide for their services, and the increased overhead and oversight from the government.

I’d be more impressed if, instead of Pres. Stompy shaking his finger at Republicans he’d actually listen to what the vast majority of Americans are bitching about regarding having their health insurance screwed with.

I’d really be impressed if ALL of Congress, including that idiot Harry Reid had to sign up with Obamacare through the exchanges. (Hey Harry, let see if you’re smart enough to use the damn internet shall we?)

NewImage

I have no idea what the hell is going on anymore. I feel like I’ve walked through the looking glass into bizzaro world.

In short, HOLY CRAP BATMAN!

NO! HELL NO!

NewImage

I got a call from Express Scripts yesterday.

God, I thought I was done with those fuckers!

It turns out that my new Obamacare sanctioned, lemon scented medical policy apparently has some kind of alliance or affiliation with Express Scripts.

I told the machine “NO! FUCK NO! I Hate you People” and hung up.

I do hope they were recording the user responses. I’d love to be in the room when someone hears that response. I’m equally sure that they hear it all the time, given the number of hits my other Express Scripts posts get on this blog.

NewImage

Express Scripts is not to be used, In fact, if my new Obamacare approved insurance policy forces me to deal with Express Scripts, I’ll change insurance carriers.

That is how strongly I feel about Express Scripts.

These people are scum and their service is best thought of as a really, really, bad Indian call center for drugs.

You might get the right information or drug… But odds are better that you’re going to get the wrong shit.

These are the people that sent me a cholesterol drug, which as it turned out I was allergic to and, oh by the way, was recalled because it was contaminated with ground glass.

Would they swap it? NOPE! The bitch on the phone actually said I’d have to put up with hives until I ran out of my 90 day supply.

I didn’t know it at the time but hives can be very dangerous.

However since I’m also not a masochist I simply didn’t take the drug. Then when the recall got announced on TV I called Express Scripts AGAIN and asked why the hell they hadn’t contacted me about the contamination of the drug.

Their answer… oh that’s the patients responsibility.

NewImage

No, I will not deal with them, not now and unless I have no other choice, NOT EVER!

I’m contacting my Doc, to find out what it would take for me to get off the few medications I take.

Yes, I know I could simply stop taking them, but I’d like to do this safely and am willing to change my habits enough so that I could stay healthy and off meds hopefully for a decade or so.

Of course, this could mean Obamacare is working…

As I’ve said elsewhere, there wont be any death panels. There will simply be people that don’t get the right meds, or effective treatments.

It will be totally random and take years for the Government to investigate why so many people are dying of “Illneses for which they were taking the correct meds.”

The answer will ultimately be; players like Express Scripts and their crappy record keeping, horrible shipping policies, and sloppy fulfillment of prescriptions caused the death of thousands.

Then there’ll be another decade of discussion and voting to improve laws governing big pharmaceutical distributors like Express Scripts during which thousands more will die.

NewImage

All the while players like Express Scripts will be driving real pharmacies and real pharmacists out of local neighborhoods and making a fortune doing it.

The inner city poor will be decimated first, when their neighborhood pharmacies close. Then it will spread to the suburbs.


Fight Companies like Express Scripts!

Refuse to cooperate, don’t comply. Raise hell if your HR department even mentions Express Scripts. Tell your insurer that you don’t want to have to deal with Express Scripts

If you’re already stuck with these bastards, check every single prescription. Question everything about them, make them earn their money, tie up phone lines and don’t use their website

Don’t take their word for anything about generics, or drugs they substitute without talking to you.

Make sure they have cleared every substitution with your physician. In my case Express Scripts lied repeatedly!

They’d never contacted my Doctor about any substitutions. I’m not talking just generics, I’m saying Express Scripts changed the drug they sent me entirely.

RESIST!

Save your neighborhood pharmacy. Save your life.

NewImage


Yeah, I’m passionate about it.

There’s something to be said for walking into your local pharmacy and actually talking to a real pharmacist who has records of what you’re taking and knows if you’re looking at a drug interaction.

Express Scripts couldn’t keep it straight, and I was using their automated reorder system.

That system was ALWAYS wrong! To make matters worse, the phone people aren’t pharmacists and they have no better access to information about what they’ve sent you than their web site, which as I’ve said was always wrong.

Medications are serious business. Get the wrong combination and you wake up in the hospital. If you wake up at all.

Yet no-one you speak to at Express Scripts has any accountability or training to answer questions other than accounting related stuff.

Worse yet, if you have a problem with a medication, when you call your doctor you’ll  have to read him or her the name of whatever it is you were taking because of the substitution some “Medical Board” made without actually examining or seeing you. Odds are they didn’t bother to send him or her any information about what you’re actually taking instead of what your doctor prescribed.

That of course presumes you can reach your doctor. What if you can’t? What if the drug interaction is severe? Do you wait it out, or do you go to an Emergency Room?

I like being able to talk to my local pharmacist. I like being able to ask questions and appreciate being warned of potential problems to watch out for. I like being forewarned and being told what to do If X, Y, or Z happen.

There are some things that big nameless, faceless, corporations simply shouldn’t be involved in.

Dispensing drugs is one of them.